
64: Ross Bagurdes: Using WireShark to Attack Hard to Find Bugs
 August 9, 2015
 Hosted by Joe Colantonio


About this episode
Introduction to Wireshark
Ross, the author of the Pluralsight course Introduction to Wireshark shows us how Wireshark can help bridge the gap between network engineers, developers and testers to ensure we are developing high-performing, secure software application awesomeness.
In this episode you’ll discover how to use WireShark to attack hard to find bugs!
About Ross
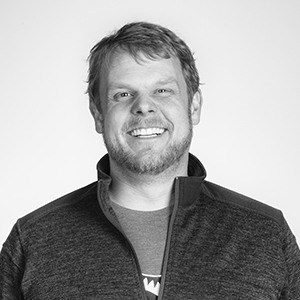
Ross has had a diverse career. He has a Structural Engineering degree from Milwaukee School of Engineering, but gave up the career shortly after graduating from college. Beginning in 1997, Ross began officially working in IT, implementing and supporting a paperless work order system for a Natural Gas Utility in Illinois. Since then, Ross has spent his years teaching and managing data networks. Ross spent 7 years at University of Wisconsin Hospitals and Clinics, supporting and managing the large enterprise network. He now has returned to teaching at Madison College in Madison, Wisconsin.
Ross is also a full-time online video instructor for Pluralsight, which offers a very wide variety of software and technical training. He has many video training courses, covering topics like data networking, how data networks work, CCNA and Wireshark.
Quotes & Insights from this Test Talk
- Wireshark is the world's foremost network protocol analyzer. It lets you see what's happening on your network at a microscopic level. It is the de facto standard across many industries and educational institutions.
- Wireshark is like, from my perspective, this bridge where it can take data networking and examine the software that's running on the data network and see if the software is behaving in a way that's consistent with the way that the protocols on the data network need to operate.
- The opportunity to understand how the data network works is pretty easy.
- As soon as you can start testing the software on the date network, you should start using Wireshark and examining how it behaves.
- Fiddler is much more geared toward HTTP type debugging. Wireshark can do all of that and more.
- Ping is a real nice protocol for beginners to work with because we can see instant results and it's real easy to pick out Ping messages in Wireshark.
Resources
Connect with Ross
- Twitter:@Bagurdes
- LinkedIn: https://www.linkedin.com/pub/ross-bagurdes/6/885/416/
- Pluralsight Courses: http://www.pluralsight.com/author/ross-bagurdes
May I Ask You For a Favor?
Thanks again for listening to the show. If it has helped you in any way, shape or form, please share it using the social media buttons you see on the page.
Additionally, reviews for the podcast on iTunes are extremely helpful and greatly appreciated! They do matter in the rankings of the show and I read each and every one of them.
Special offer for TestTalks listeners, get 20 hours of automated testing for free when you sign-up with promo code testtalks14 (more info).
Keep listening
Related episodes
Automation Testing Podcast · Ep. 609
Why Your AI Tests Pass When Your Features Fail with Donovan Brady
with Donovan Brady
Why Your AI Tests Pass When Your Features Fail? Donovan Brady of Leapwork shows how to make
Oct 27
Automation Testing Podcast · Ep. 608
Scary Test Automation POCs Made Easy: Halloween Special With Paul Grossman
with Paul Grossman
Running a proof of concept on test automation tools can feel like a horror movie. Vendors promise
Oct 20
Automation Testing Podcast · Ep. 607
Locust and Azure Load Testing: Create and Debug Load Tests with AI with Lars Holmberg and Abhinav Premsekhar
with Lars Holmberg and Abhinav Premsekhar
Performance testing has never been easier to start, or more important to get right. As teams ship
Oct 6
Automation Testing Podcast · Ep. 606
AI Agents Passed the Tests. Real Devices Didn’t. with Nick Metcalfe
with Nick Metcalfe
Cloud device farms make it easy to get started with real device testing. But what happens when
Sep 29