
21: Troy Hunt: Hack Your API-Security Testing
 September 28, 2014
 Hosted by Joe Colantonio
About this episode
How to hack your APIs Are you doing all you can to ensure that your APIs are secure? If you haven’t started security testing yet, now is the time. It is estimated that by 2020 there will be more than 50 billion objects connected to the Internet, and most of those objects will be using APIs. Not sure where to start?
Troy Hunt, author of the Pluralsight course Hack Your API First, shares all you need to know about the basics of API security testing, including the tools and techniques you’ll need to quickly get started. Troy’s motto is, “Hack yourself before you get hacked!”
About Troy Hunt
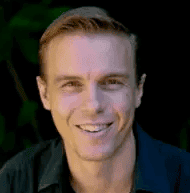
Troy is a Software Architecture Lead for a Fortune 50 healthcare company, Microsoft MVP for Developer Security and ASPInsider who's been building software for browsers since the very early days of the web. He blogs regularly about web security at troyhunt.com and is the author of the OWASP Top 10 for .NET developers series and the free eBook of the same name. He's also a frequent conference speaker and the creator of the Automated Security Analyzer for ASP.NET Websites (ASafaWeb) at asafaweb.com. Away from electronic devices, Troy is an avid snowboarder, windsurfer, tennis player and regular motor sport participant.
Quotes & Insights from this Test Talk
- The earlier we can find security issues in the APIS we’re developing, the better.
- It’s a good idea to have a dedicated security professional on your team.
- The life of an app doesn’t end after we release; ongoing, continuous monitoring is always a good idea.
- Never get lulled into thinking your API/Application is safe; it’s kind of like saying your car is safe. Validation is needed on the client and the server.
- Just look at the HTTP request and forget about the client, and see what you can find.
- You’ve got to assume that an attacker owns the device and the connection, and he can manipulate anything on either the client or server side.
- Not expecting your services to be discoverable is a common blind spot in API security.
- Returning excessive data is a common issue with Rest service security.
Resources
- OWASP
- Hack Your API First – Must view training for API security testing
Tools
- Fiddler – a free web debugging proxy for any browser, system or platform
- Wireshark
- Metasploit
Connect with Troy
- Twitter: @TroyHunt
- Troy's blog – http://www.troyhunt.com/
May I Ask You For a Favor? Thanks again for listening to the show. If it has helped you in any way, shape or form, please share it using the social media buttons you see on the page. Additionally, reviews for the podcast on iTunes are extremely helpful and greatly appreciated! They do matter in the rankings of the show and I read each and every one of them.
Keep listening
Related episodes
Automation Testing Podcast · Ep. 609
Why Your AI Tests Pass When Your Features Fail with Donovan Brady
with Donovan Brady
Why Your AI Tests Pass When Your Features Fail? Donovan Brady of Leapwork shows how to make
Oct 27
Automation Testing Podcast · Ep. 608
Scary Test Automation POCs Made Easy: Halloween Special With Paul Grossman
with Paul Grossman
Running a proof of concept on test automation tools can feel like a horror movie. Vendors promise
Oct 20
Automation Testing Podcast · Ep. 607
Locust and Azure Load Testing: Create and Debug Load Tests with AI with Lars Holmberg and Abhinav Premsekhar
with Lars Holmberg and Abhinav Premsekhar
Performance testing has never been easier to start, or more important to get right. As teams ship
Oct 6
Automation Testing Podcast · Ep. 606
AI Agents Passed the Tests. Real Devices Didn’t. with Nick Metcalfe
with Nick Metcalfe
Cloud device farms make it easy to get started with real device testing. But what happens when
Sep 29